Search News
Global Industrial Intelligence Hub (GIIH)Industry Portal
Global Industrial Intelligence Hub (GIIH)Status
Standard Access
Upgrade to PremiumNewsEU Tightens Cybersecurity Certification for IoT Home Devices
Time
Click Count
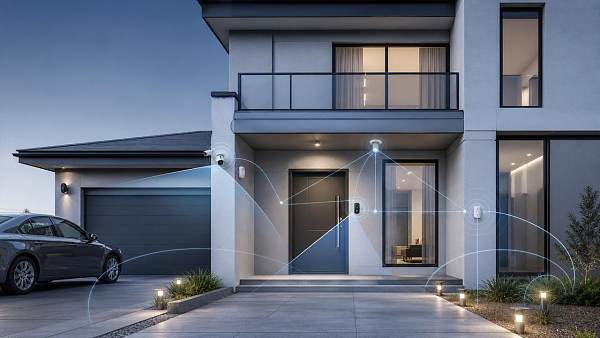
As of August 1, 2026, the EU has moved CRPA into full implementation as a supporting measure under the Cyber Resilience Act (CRA), bringing a concrete compliance threshold for IoT home devices sold into the EU market. For manufacturers, exporters, distributors, procurement teams, and compliance service providers involved in smart security, home automation, and smart lighting products, this is worth close attention because the change is no longer a policy signal alone; it now affects market access, customs clearance, listing readiness, and supporting documentation for product delivery.
What the Rule Now Requires at Market Entry
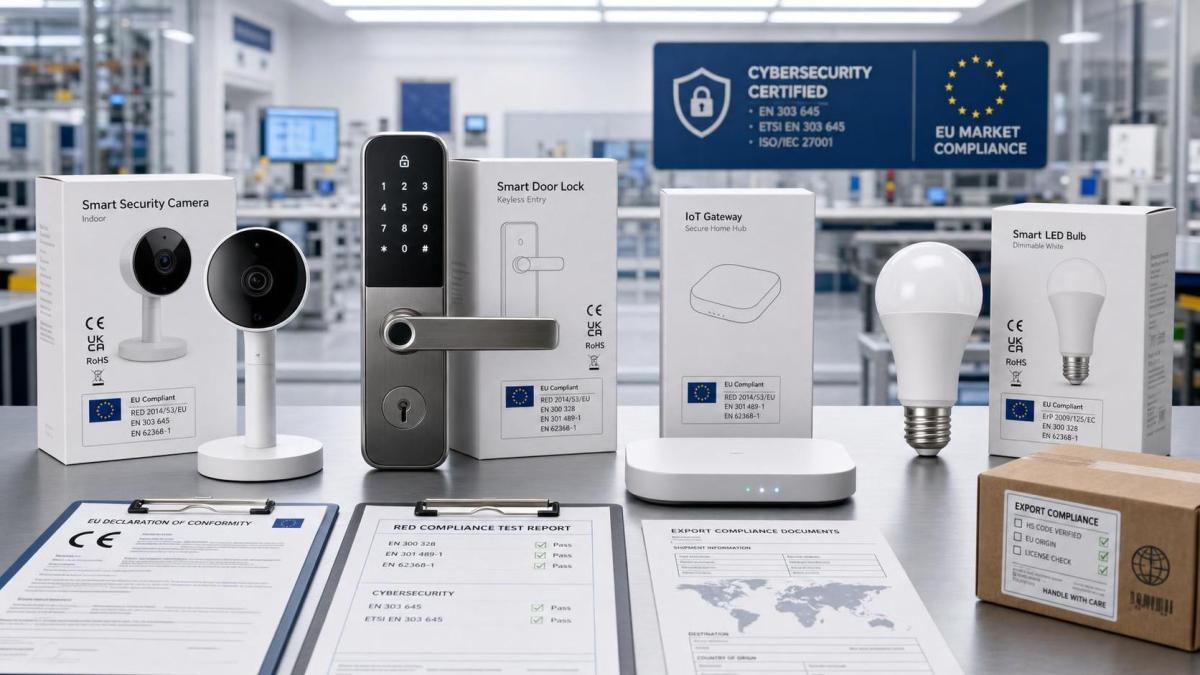
According to the confirmed information provided, the CRPA implementing regulation under the Cyber Resilience Act took effect on 2026-08-01. It requires all IoT home devices sold in the EU market, including smart security, home automation, and smart lighting products, to complete CRA compliance assessment and carry both the CE and CR marks.
The rule also requires manufacturers to provide a vulnerability disclosure mechanism, a commitment to security updates, and proof of lifecycle support. Products that do not comply will not be allowed to clear customs or be listed for sale.
Where the Pressure Will Be Felt Across the Supply Chain
For product manufacturers, compliance moves closer to product definition
From an industry perspective, manufacturers are likely to face the most direct impact because the new requirement is tied to whether a product can enter and remain in the EU market. The affected business steps are not limited to final labeling. They extend to compliance assessment, technical documentation preparation, proof of support commitments, and the internal arrangements needed to handle vulnerability disclosure and security updates.
What deserves closer attention is that these requirements may influence how product specifications, release timing, and after-sales support commitments are organized before shipment.
For exporters and channel operators, shipment and listing risks become more immediate
Export businesses and distribution channels may be affected because non-compliant products are stated to face both customs and sales restrictions. In practical terms, the main exposure is likely to sit in pre-shipment review, customs documentation readiness, listing qualification, and coordination with manufacturers over whether the required marks and supporting materials are complete.
Analysis shows that for these roles, compliance is not only a product issue but also a delivery risk issue, especially where sales arrangements depend on products reaching shelves or online listings on schedule.
For procurement and supply-chain coordination, supplier qualification may tighten
Procurement teams and supply-chain service providers may need to pay closer attention to whether suppliers can demonstrate CRA compliance assessment status, CE+CR marking readiness, and the required cybersecurity support commitments. The impact may appear in supplier onboarding, purchase order conditions, delivery acceptance, and supporting document review.
Observably, the rule may also affect how buyers evaluate whether a supplier can support post-sale obligations tied to vulnerability handling and security updates, rather than only the physical delivery of the device itself.
For testing, certification, and after-sales support functions, documentation matters more
Certification-related service providers, testing support functions, and after-sales teams may also see a shift in workload. The reason is that the confirmed requirements go beyond a one-time product check and explicitly include vulnerability disclosure, security update commitments, and lifecycle support proof. These points may increase attention on document consistency, support statements, and traceability across the product lifecycle.
What Companies Should Review Now
Check whether current product files can support CRA assessment
Analysis shows that companies selling relevant IoT home devices into the EU should first review whether existing technical files and compliance materials are sufficient for CRA assessment and CE+CR marking. Where the input information does not provide detailed execution criteria, it is more appropriate to treat this as a prompt to verify documentation completeness rather than to assume a uniform review standard has already formed.
Review how security commitments are expressed in commercial and technical documents
What deserves closer attention is whether product documents, bid materials, declarations, after-sales terms, and related technical statements clearly align with the required vulnerability disclosure mechanism, security update commitment, and lifecycle support proof. If these statements are inconsistent, the issue may affect both compliance review and downstream customer acceptance.
Reassess delivery scheduling for EU-bound products
Observably, products intended for the EU market may require a tighter link between compliance readiness and shipment planning. Companies should pay attention to whether certification-related preparation, mark application, and supporting materials are ready before customs and listing stages. The confirmed information does not specify operational timelines beyond the effective date, so execution rhythm still needs to be monitored in practice.
Track how purchasers and channels update their entry requirements
From an industry perspective, another practical point is whether procurement documents, supplier qualification standards, and channel listing conditions begin to reflect the new rule more explicitly. The input does not provide examples of such changes, so this remains an area for active monitoring rather than a confirmed market-wide outcome.
Why This Looks Like an Execution Signal, Not Only a Policy Update
Analysis shows that this development is more appropriately understood as a rule entering the execution stage for EU market access in the IoT home device segment. The reason is straightforward: the confirmed information links compliance directly to customs clearance and sales listing, which shifts the discussion from general regulatory direction to actual transaction and delivery consequences.
At the same time, it would be premature to treat all implementation details as settled. Observably, the market still needs to watch how compliance review is applied in practice, how supporting documents are examined, and how buyers, channels, and service providers translate the rule into their own operating requirements.
How to Read This Development at the Current Stage
At this stage, the industry significance lies in the fact that cybersecurity compliance for IoT home devices in the EU is no longer only a design or legal topic; it has become a market-entry condition tied to shipment, listing, and support commitments. A neutral reading is that the rule now represents a landed compliance requirement with direct commercial implications, while many execution details still need continued observation through market practice and follow-on guidance.
Basis of This Article and What Still Needs Verification
This article is based on the user-provided news title, event date, and event summary. For developments of this kind, relevant information is typically associated with source categories such as official announcements, regulatory publications, customs or trade authority notices, industry association updates, standards documents, and reporting by authoritative media.
No specific official source link was provided in the input, so the exact official reference still needs further verification. It remains necessary to continue watching later details such as implementation guidance, certification interpretation, changes in tender or procurement documents, industry feedback, and how companies are handling compliance in actual delivery processes.
Recommended News
 Sep 05, 2026Which Smart Living Device Categories Are Growing Fastest in 2026?What Smart Living device categories are growing fastest in 2026? Explore high-demand opportunities in security, energy management, automation, care monitoring, and smart appliances.
 Aug 24, 2026US Imposes 100% Additional Tariff on Certain Drones Effective August 13US imposes 100% additional tariff on certain drones effective August 13. Learn which drone products are covered, the compliance risks, and how importers and exporters should respond now.
 Aug 23, 2026When does facial recognition access make sense for home entry security?Facialrecognitionaccess makes sense when your home needs fast, hands-free entry for multiple residents. Discover when it improves convenience, privacy, and daily security.
 Aug 20, 2026What drives IoT home security price from basic setups to smart systemsIoT home security price depends on hardware, connectivity, AI features, installation, and subscriptions. Learn what raises costs and how to choose smarter value.
 Aug 10, 2026What Range and Signal Factors Matter Most in Long Range Home Systems?Long range home systems perform best when range, frequency, interference, wall materials, and placement work together. Learn what really affects reliable coverage before you buy.
 Aug 09, 2026EU CE Rule Takes Effect for IoT Home Security DevicesEU CE Rule for IoT Home Security Devices takes effect: learn how EN 303 645:2026 impacts CE marking, compliance, cybersecurity, suppliers, and EU market access.
 Aug 08, 2026EU Enforces EN 303 645:2026 v2.1 for IoT Security DevicesEN 303 645:2026 v2.1 now shapes EU access for IoT security devices. Learn how the new certification rules affect customs clearance, firmware checks, and shipment timelines.
 Aug 07, 2026EU CE Rule Takes Effect for IoT Home Security DevicesEU CE Rule takes effect for IoT home security devices in 2026. Learn how EN 303645-2, ETSI TS 103 645, and Notified Body certification will impact EU market access.
 Aug 06, 2026EU EN 303645-2:2026 Takes Effect for Home IoT SecurityEU EN 303645-2:2026 takes effect for home IoT security on Nov 1, 2026. Learn how CE-RED+Cybersecurity Module and remote diagnostic interface rules impact EU market access.
 Aug 05, 2026EU WEEE Rules Add Remote Diagnostics for IoT Home DevicesEU WEEE rules now require remote diagnostics and firmware upgrade interfaces for IoT home devices. Learn the compliance risks, CE impact, and how exporters can avoid EU customs rejection.
 Aug 04, 2026EU Tightens RoHS Lead Limits for IoT Home DevicesEU Tightens RoHS Lead Limits for IoT Home Devices: learn how the new EU RoHS amendment impacts smart lighting, home security, testing, sourcing, and compliance timelines.
 Aug 03, 2026EU Extends WEEE Duties to IoT Home ExportersEU Extends WEEE Duties to IoT Home Exporters: learn how the 2027 EU WEEE revision impacts smart home compliance, authorized representatives, costs, and market access.
 Aug 02, 2026EU Tightens Cybersecurity Certification for IoT Home DevicesEU Tightens Cybersecurity Certification for IoT Home Devices: learn how CRA and CRPA rules affect CE+CR marking, customs clearance, and EU market access before 2026.
 Aug 01, 2026EU Requires CRA Certification for IoT Home DevicesEU CRA certification for IoT home devices is now critical for smart locks, cameras, and alarms entering the EU. Learn the compliance risks, CE+CRA marking needs, and supply chain actions to protect market access.
 Jul 22, 2026How to Choose a Smart Access Control Terminal for Offices, Factories, and WarehousesSmart access control terminal buying guide for offices, factories, and warehouses. Learn how to compare security, integration, resilience, and scalability for smarter site decisions.
 Jul 15, 2026Commercial Office Home Control Systems: What Features Matter Most in Daily UseCommercial office home control systems work best when daily use stays simple. Learn which features improve efficiency, reduce errors, and support smarter office operations.
 Jul 14, 2026Smart Home Protection App Control: Key Functions, Setup Steps, and Common IssuesSmart home protection app control made simple: explore key functions, setup steps, common issues, and practical fixes to improve security, reliability, and peace of mind.
![]() Jul 07, 2026Smart Access Control Price Guide: What Affects System Cost for Homes, Offices, and Sites?Smart access control price guide for homes, offices, and multi-site projects. Learn what drives system cost, from hardware and installation to software, integration, and long-term value.
 Jul 04, 2026Flame Retardant Home Systems: Key Ratings, Materials, and Installation MistakesFlame retardant home systems explained: compare key fire ratings, common materials, and costly installation mistakes to choose safer, compliant solutions.
 Jul 03, 2026Smart Technology Access Control: Which System Fits Multi-Entrance Buildings Best?Smart technology access control for multi-entrance buildings: compare cloud, mobile, biometric, and hybrid systems to find the best fit for security, flow, scalability, and cost.
 Jul 02, 2026Metal Housing Smart Access Control: What to Check for Outdoor and High-Traffic SitesMetal housing smart access control: learn what to check for outdoor and high-traffic sites, from weather resistance to integration and lifecycle cost, before you choose.
 Jun 29, 2026Global Connected Home Technology Standards: Interoperability, Security, and Certification BasicsGlobal connected home technology standards shape interoperability, security, and certification success. Learn the basics to reduce launch risk, speed approvals, and improve cross-market product reliability.
 Jun 25, 2026Flame Retardant Connected Home Technology: Which Standards and Materials MatterFlame retardant connected home technology explained: compare key standards, materials, and compliance risks to build safer smart devices and speed market access.
 Jun 08, 2026How to Choose Wireless Security Systems for Homes: Cameras, Sensors, and CoverageWireless security systems for homes made simple: learn how to choose cameras, sensors, and coverage that fit your layout, budget, and daily routine for smarter protection.